Tags
6 pages
PHP
Quote-less, digit-less PHP eval sandbox escape to RCE - Nullcon Berlin 2025
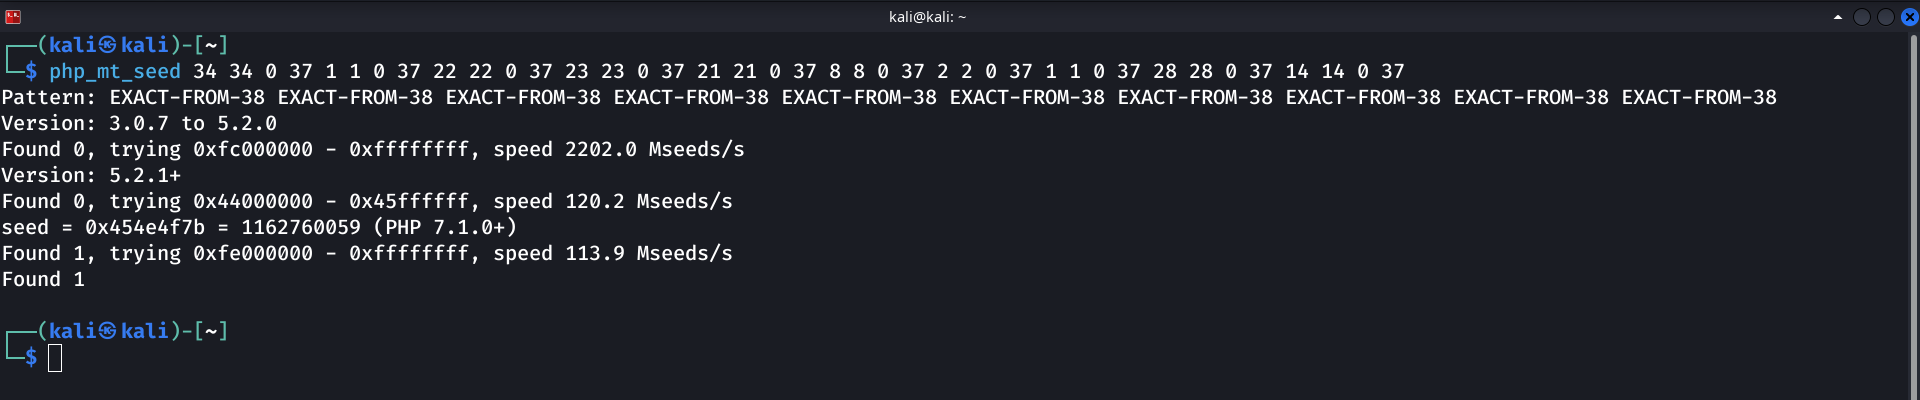
Reversing PHP mt_rand() to recover a flag from session IDs - Nullcon Goa 2025
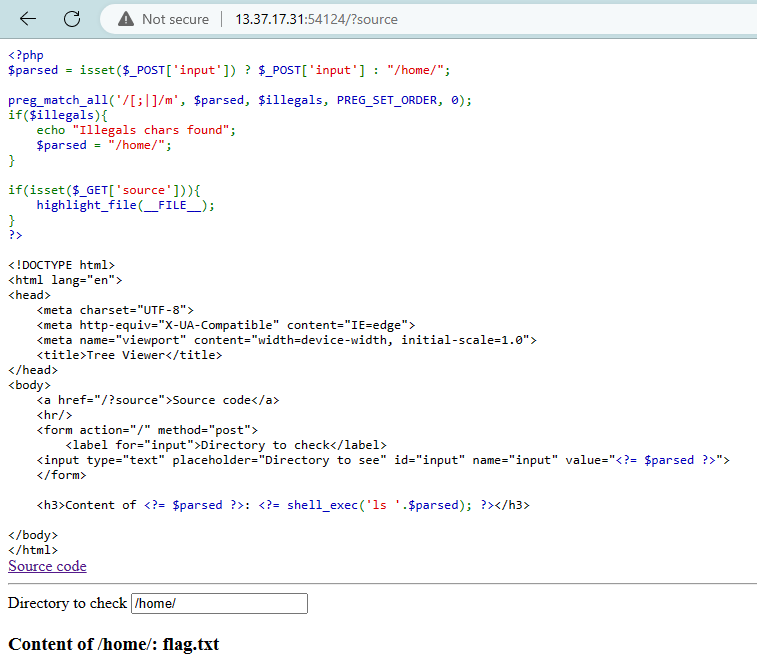
Bypassing a preg_match filter for command injection - PwnMe 2023
Command injection via a QR generator's size parameter - PwnMe 2023
PHP integer overflow to force a negative sum - Nullcon Goa 2025
CRC32 hash collision to defeat a PHP password check - Nullcon Goa 2025