Categories
24 pages
Web
HTTP keep-alive request smuggling past auth (unintended) - ImaginaryCTF 2025
Quote-less, digit-less PHP eval sandbox escape to RCE - Nullcon Berlin 2025
GraphQL mass-assignment privilege escalation in Next.js - snakeCTF 2025
X-Forwarded-For 403 bypass and Flask session forgery - Pragyan CTF 2025
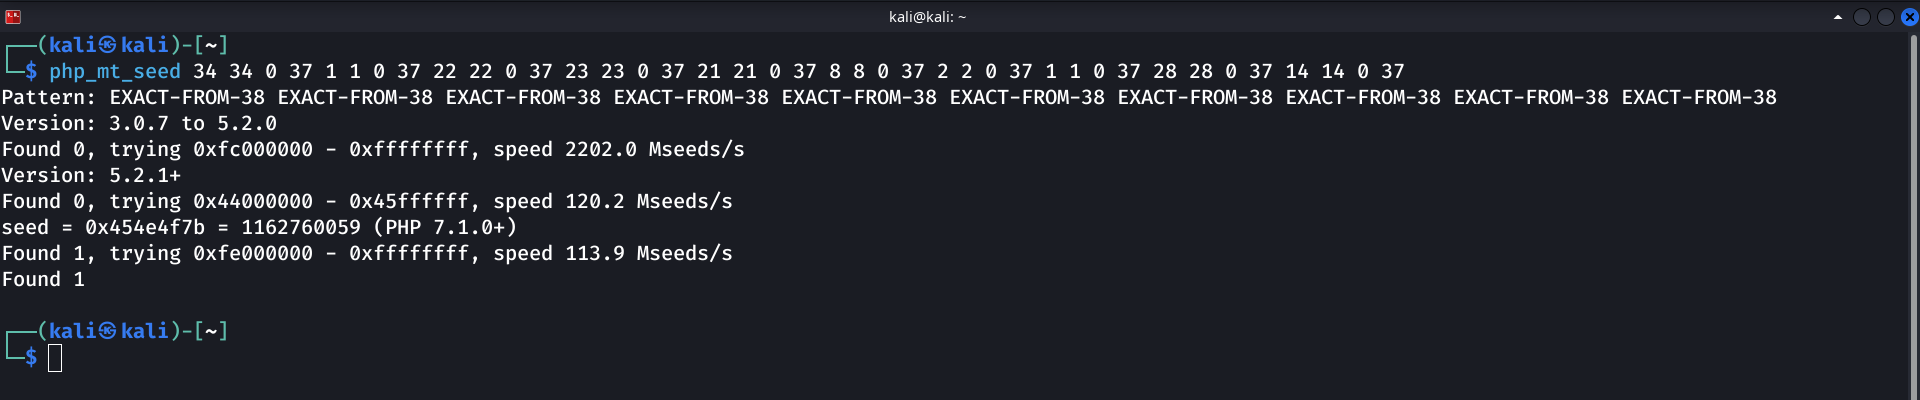
Reversing PHP mt_rand() to recover a flag from session IDs - Nullcon Goa 2025
GraphQL alias batching to bypass a rate limit - HeroCTF v5
Bypassing a preg_match filter for command injection - PwnMe 2023
Perl two-argument open command execution - ImaginaryCTF 2025
TOCTOU race to bypass MFA in a web.py login - Nullcon Berlin 2025
API mass assignment to admin and a restricted chat - snakeCTF 2025
1
2
3
Jump to page
(1 - 3)
Go
Enter
Press Enter to jump