Categories
2025
Supabase anon key and missing RLS data leak - ImaginaryCTF 2025
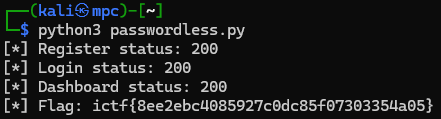
bcrypt 72-byte truncation and email normalization auth bypass - ImaginaryCTF 2025
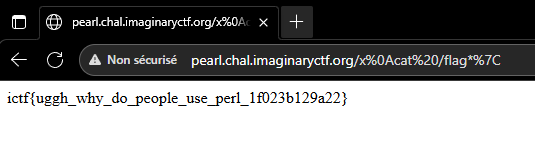
Perl two-argument open command execution - ImaginaryCTF 2025
HTTP keep-alive request smuggling past auth (unintended) - ImaginaryCTF 2025
TOCTOU race to bypass MFA in a web.py login - Nullcon Berlin 2025

Quote-less, digit-less PHP eval sandbox escape to RCE - Nullcon Berlin 2025
Racing a custom CAPTCHA gate with concurrent requests - snakeCTF 2025

API mass assignment to admin and a restricted chat - snakeCTF 2025

GraphQL mass-assignment privilege escalation in Next.js - snakeCTF 2025

Jinja2 SSTI in a card generator - Pragyan CTF 2025
X-Forwarded-For 403 bypass and Flask session forgery - Pragyan CTF 2025
CRC32 hash collision to defeat a PHP password check - Nullcon Goa 2025
PHP integer overflow to force a negative sum - Nullcon Goa 2025
Source leak and Python SSTI to the flag - Nullcon Goa 2025
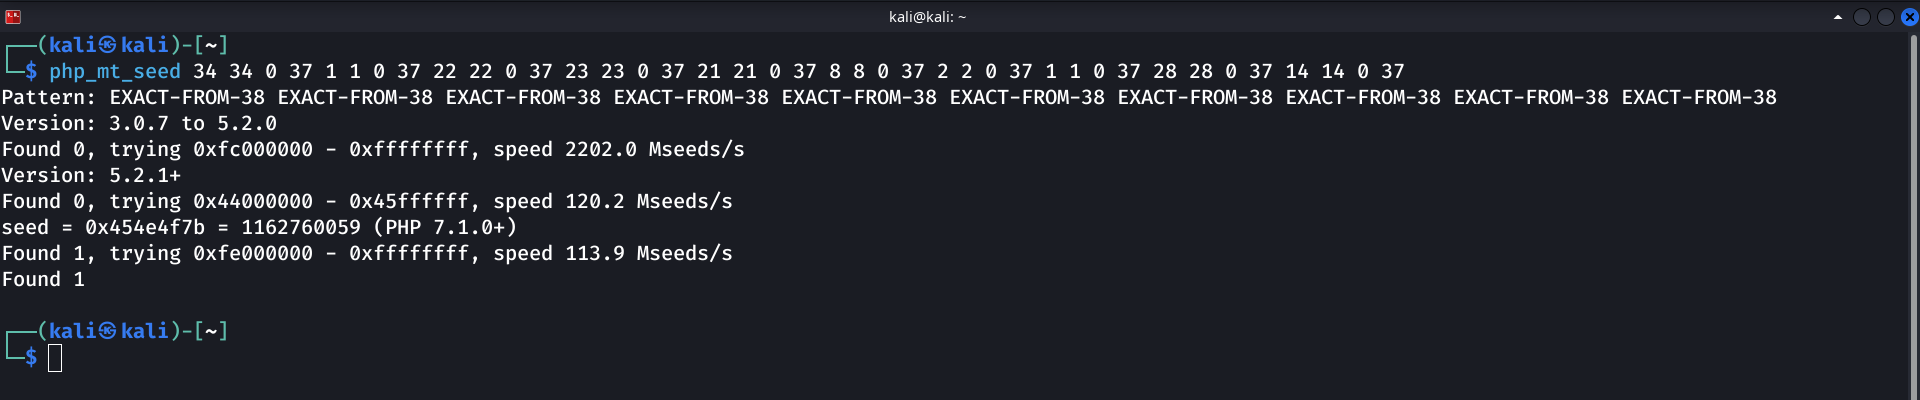
Reversing PHP mt_rand() to recover a flag from session IDs - Nullcon Goa 2025
2024
Stored XSS, cache poisoning and password reset to admin takeover - HeroCTF v5
Author enumeration and a guessable referral secret - HeroCTF v5
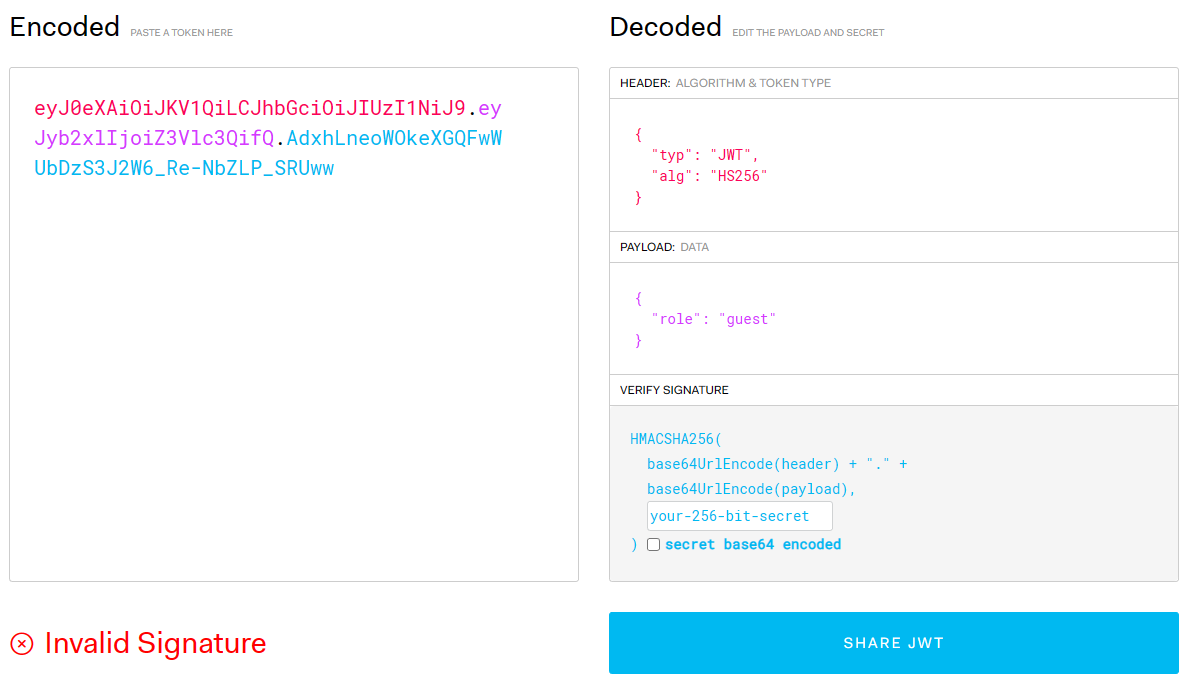
Cracking a weak JWT secret into Jinja2 SSTI RCE - HeroCTF v5
Referer-based auth bypass via an Nginx/Express misconfig - HeroCTF v5
GraphQL alias batching to bypass a rate limit - HeroCTF v5
2023
Source disclosure to Jinja2 SSTI RCE on Flask - PwnMe 2023
Geolocating three cities from a target's social posts - PwnMe 2023

Tracing a target's life across social media - PwnMe 2023

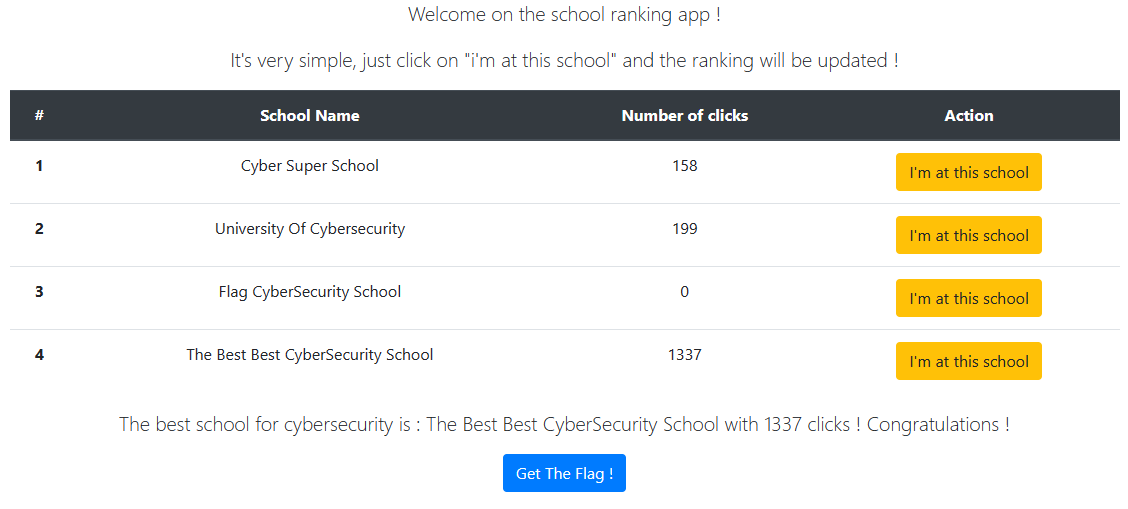
Forging a client-side score to beat an unbeatable game - PwnMe 2023

From a username to an exposed .git repository - PwnMe 2023

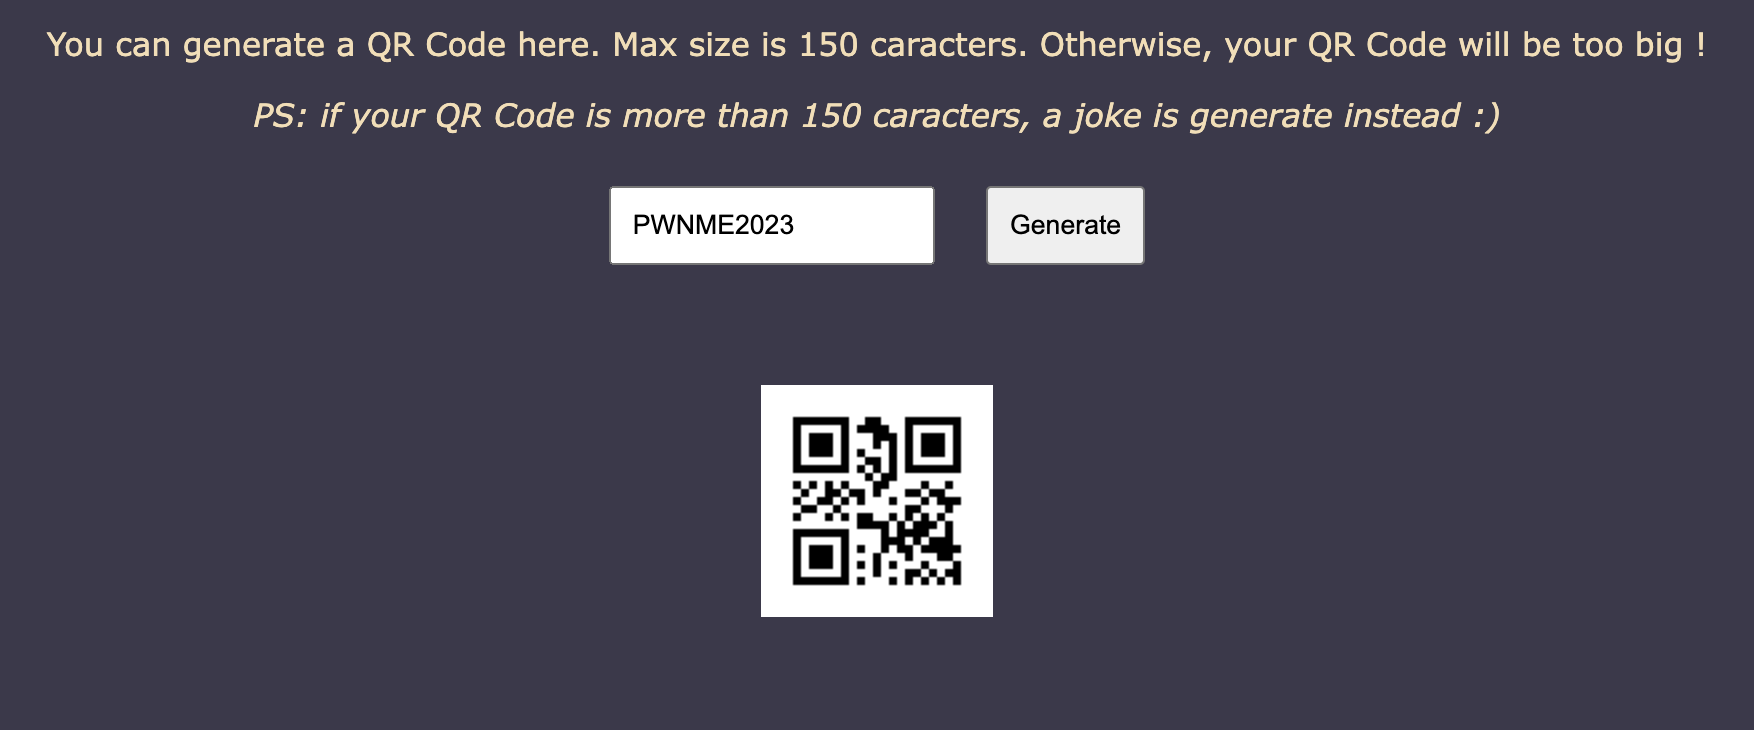
Command injection via a QR generator's size parameter - PwnMe 2023
Pivoting a bilingual target's social accounts - PwnMe 2023

Bypassing a preg_match filter for command injection - PwnMe 2023