A deep dive into the Windows Antimalware Scan Interface (AMSI): its architecture, the amsi.dll API, how scan providers plug in, and why that design is the thing you end up abusing in part 2.
An unintended keep-alive bug: a stale client_addr lets you smuggle a privileged request past the auth check. ImaginaryCTF 2025.
Escaping a PHP eval sandbox with a quote-less, digit-less function chain to reach RCE. Nullcon Berlin HackIM 2025 web write-up.
Privilege escalation via user-controlled settings in a Next.js GraphQL pastebin (isAdmin:true). snakeCTF 2025 Quals web write-up.
Brute-forcing a Flask admin panel behind an XML employee list to turn a 403 into a 200. Pragyan CTF 2025 web write-up.
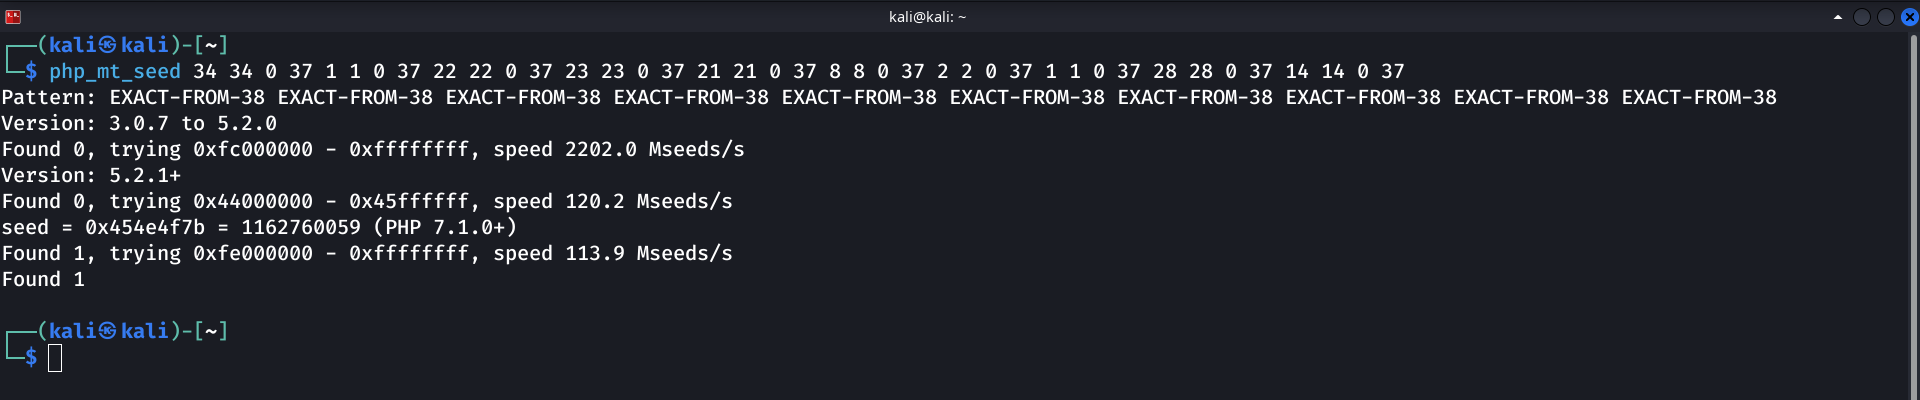
Reversing PHP mt_rand() with php_mt_seed to recover a flag leaked through session IDs, chunk by chunk. Nullcon Goa HackIM 2025.
Abusing GraphQL alias batching to bypass a rate limit and stuff a voting endpoint into first place. HeroCTF v5 web write-up.
Bypassing a preg_match filter over shell_exec to read flag.txt via command injection. PwnMe 2023 web write-up.
Pivoting across a bilingual target's social accounts where key information hides in only one language. PwnMe 2023 OSINT write-up.
Abusing Perl's two-argument open for command execution via a trailing pipe and newline injection. ImaginaryCTF 2025 web write-up.